Protect digital wallets and the value stored inside them
A wallet app holds tokens, balances and payment credentials on a device you do not control. SecIron keeps that value safe by hardening the app, detecting runtime attacks and showing you where fraud is being attempted.
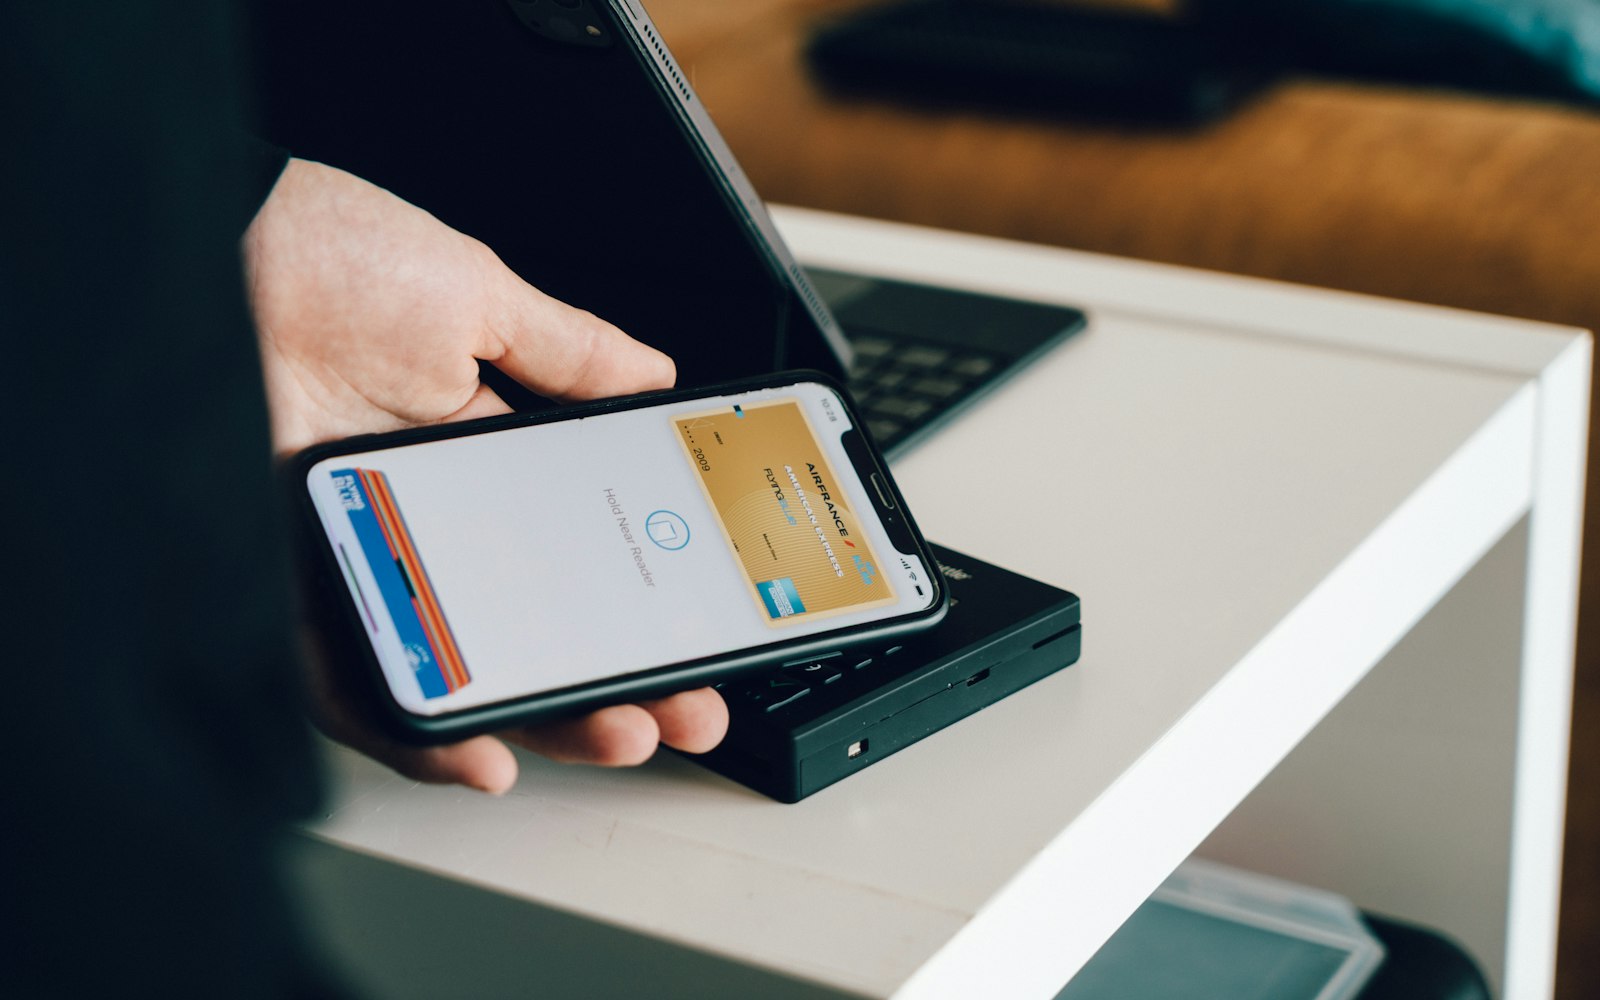
Balance, tokens and keys all live on the handset
A wallet app holds the things an attacker wants most: stored value, payment tokens and the keys that authorise them, on a device that may already be rooted or running an overlay.
SecIron hardens the compiled wallet so stored secrets stay unreadable, detects tampering and instrumentation while the app runs, and reports every attempt to your fraud team as it happens.
How wallets get drained
Wallet fraud rarely needs a breach of your back-end. It needs a copy of your app, a rooted phone and a few hours with freely available tools.
Extracted tokens and keys
Decompiling the app to find where payment tokens, API keys and encryption keys live, then lifting them for use outside the app.
Cloned wallet apps
A repackaged copy that looks identical, collects PIN and OTP, and forwards them to the attacker.
Runtime manipulation
Hooking frameworks that change balances on screen, skip transaction limits or bypass PIN and biometric checks.
Emulator and bot farms
Thousands of wallet instances on emulators used to farm sign-up bonuses, cashback and referral rewards.
Man-in-the-middle on top-ups
Stripped certificate pinning lets attackers intercept and replay top-up, transfer and QR payment calls.
Overlay and screen capture
Malware that draws a fake PIN pad over your real one or records the screen during a transaction.
Protection that travels with the wallet
Three layers, one platform. Assessment finds the weaknesses, hardening removes them from the build and monitoring tells you what attackers try next.
Assess with IronSCAN
Find insecure storage, weak crypto and exposed endpoints before the wallet ships.
- Credentials and tokens stored in the clear
- Hard-coded keys and secrets
- Missing or weak certificate pinning
Harden with IronWALL
Harden the compiled wallet in minutes with no code changes.
- Obfuscation, encryption and integrity checks
- Anti-hooking, anti-debugging, anti-tampering
- Root, emulator, overlay and screen-capture detection
Monitor with IronSKY
See every attack on the wallet by device, region and method.
- Emulator-farm and cloned-app alerts
- Device risk signals for transaction decisions
- Evidence for fraud and compliance teams
How teams like yours protect their apps with SecIron
The protection that keeps balances, transfers and card data safe in a banking app applies to every wallet. See how one bank did it.
 International bankCase study · BankingHow SecIron helped an international bank meet its mobile security mandatesA central regulatory mandate required every banking app to be protected, within weeks. IronWALL was deployed on-premise for iOS and Android, with no SDK and no source code changes, so the bank could harden its app without slowing a single release.2 weeksto the first protected appMinutesto harden every update0source code changesRead the case study
What changes once the app is protected
| Scenario | Before SecIron | With SecIron |
|---|---|---|
| Tokens extracted from the APK | Keys reused to script payments from outside the app | Secrets encrypted and bound to the hardened app; extraction attempts are detected |
| Cloned wallet in a third-party store | Customers lose PIN and OTP to a fake | Integrity check fails on launch; clone cannot run and is reported to IronSKY |
| Emulator farm claiming sign-up rewards | Promotion budget drained by bots | Emulators detected at runtime; sessions blocked and devices flagged |
| PIN pad overlay on a user device | Credentials captured during top-up | Overlay detected; the app blocks the screen or warns the user |
| Regulator asks for mobile channel evidence | A pen-test PDF from last year | Continuous attack telemetry plus IronSCAN assessment reports |
Frequently asked
Can SecIron protect the wallet SDK we embed in partner apps?
Yes. SecIron offers SDK-level protection for third-party or proprietary modules, including wallet and payment modules embedded in partner apps and mini apps inside super apps.
Will protection affect app performance?
Modern hardening is designed to provide strong security with minimal impact on performance. Implemented correctly, users experience little to no noticeable difference in launch time or responsiveness.
Do our developers need to change code?
No. IronWALL protection is codeless: you upload the compiled APK, AAB or IPA, select the protection modules and receive a hardened build. There is no SDK to wire in and no source code access required.
Can SecIron run in our own environment?
Yes. SecIron can be deployed on-premise or in a private cloud for organisations that cannot send application binaries or telemetry outside their own environment.
Resources for digital wallet teams
Guides, research and practical checklists from the SecIron team.
 BlogHow to protect Android apps from mobile overlay attacksRead the article →
 BlogSecuring mobile applications against banking trojan malware attacksRead the article →
 GuideProtecting mobile apps against malware: a 16-page guideRead the article →
Browse all blog posts, success stories and whitepapers and guides.
See it on your own app
Send us a build and we will harden it live, so your team can judge the protection and the performance impact before you decide.
End-to-end mobile application security. Assess, harden and monitor Android and iOS apps with codeless integration.