05 Nov
Accessibility Service Abuse: Android 17 Changes Wh...
Accessibility is the most valuable permission an attacker can obtain on Android. What Android 17 restricts, why the installed base means it is not enough yet, and what your app should detect.
04 Nov
Malaysia Steps Up Cybersecurity Preparedness: What...
Malaysia has heightened its cybersecurity preparedness amid geopolitical tensions. What it means for government, banking, energy, transport and insurance, and why mobile application security belongs in the resilience plan.
03 Nov
OWASP Mobile Top 10: A Practical Guide to Mobile A...
The OWASP Mobile Top 10 explained in practical terms: what each mobile application security risk is, how it shows up in a real banking app, and what closes it.
01 Nov
App Tampering: What It Costs and Who Pays
App tampering losses are usually filed as fraud, marketing overspend or underwriting. The four business outcomes, why cloning costs most, and the three figures that make the case.
29 Oct
NFC Relay and Ghost Tap: The New Payment Fraud Cha...
NFC relay borrows a real card in real time rather than stealing it for later. The five-step chain, why card fraud analytics cannot see it, and what detects it on the device.
25 Oct
Mobile Reverse Engineering: How Attackers Read You...
Mobile reverse engineering is the first step in almost every serious attack on an app. Static versus dynamic analysis, what each platform gives up, what AI changed, and how to defend both halves.
22 Oct
Top Mobile App Security Threats For The Banking In...
Top Mobile App Security Threats For The Banking Industry Digitalization is in full swing in the fintech, eWallet providers, and banking industry, and it’s brought along numerous benefits to financial institutions. Lack of security is a significant problem for all
22 Oct
A 30-Day Mobile App Compliance Preparation Plan
A four-week plan to move from having mobile app controls to proving them. Inventory, harden, learn from your telemetry, then enforce, with the evidence pack an examiner asks for.
22 Oct
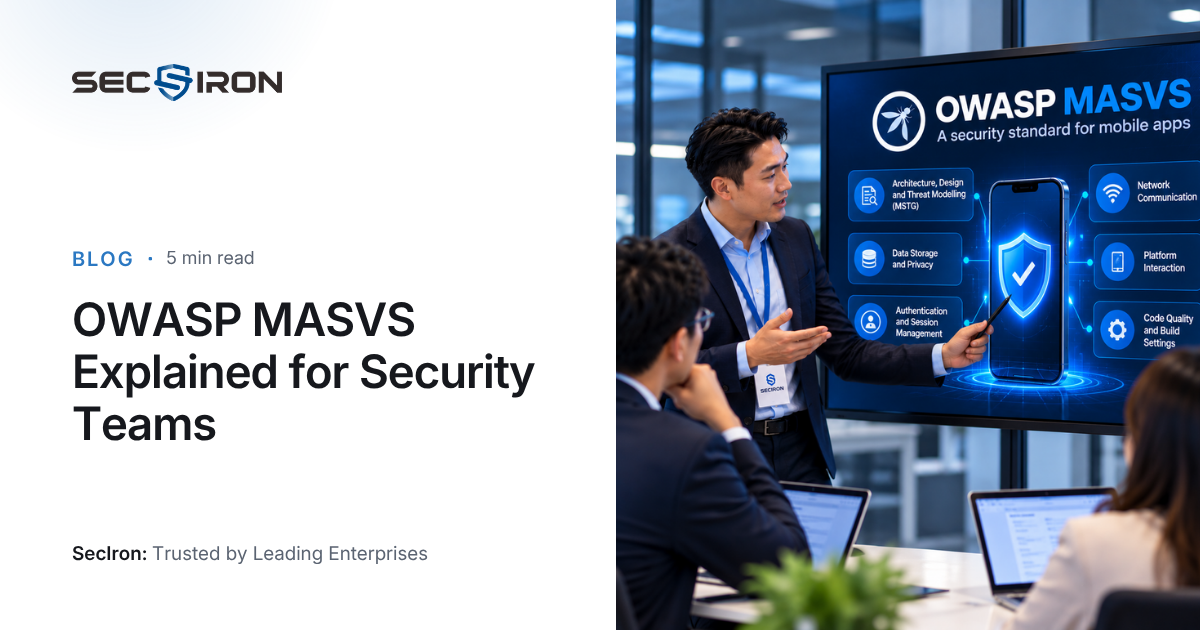
OWASP MASVS Explained for Security Teams
OWASP MASVS is cited more often than it is read. What the control groups cover, why the resilience group changes the conversation, and how to use it without creating a spreadsheet.
18 Oct
Mobile Application Hardening: Build vs Buy
Any competent team can build hardening. Few can maintain it through four OS releases while shipping a roadmap. The recurring costs, when building is right, and the hybrid most teams land on.
Recent Posts