Mobile app security for connected cars and drivers
The driver’s app talks to the car. Secure the connection between the connected vehicle, the mobile application and your digital network, from unlock to telematics, with protection that does not change a line of code.
The connected security for cars, drivers and makers
A secure connectivity platform lets car manufacturers support current and future services and applications. The driver’s mobile app is now a key, a dashboard and a service channel in one, and it runs on a phone the manufacturer does not control, where it can be decompiled, modified and used to reach the vehicle’s onboard systems.
SecIron secures that app: assessment finds the weaknesses, hardening makes the binary resistant to tampering and reverse engineering, and monitoring shows your team every attempt to interfere with the connection between driver and car.

What attackers do to automotive apps
Connected-car applications are attacked through the app code, the runtime environment and the device. Understanding these threats is the first step toward a safe, secured driving experience.
Reverse engineering
Decompiling the driver app to extract vehicle protocols, pairing keys and the commands that unlock, start and configure the car.
Tampered control apps
Modified builds that issue unauthorised commands to the vehicle, bypass checks or redirect telematics to an attacker.
Onboard system access
Attacks that pivot from the mobile app into the vehicle’s digital pipelines, such as the media centre or CAN bus interfaces.
Credential and token theft
Driver and vehicle credentials lifted from the app and reused to locate, track or access a car.
Runtime manipulation
Hooking and instrumentation on rooted or jailbroken phones intercepting commands between the app and the vehicle.
UNECE WP.29 and standards
New manufacturing and digital infrastructure standards that require OEMs and vendors to conform to cybersecurity requirements globally.
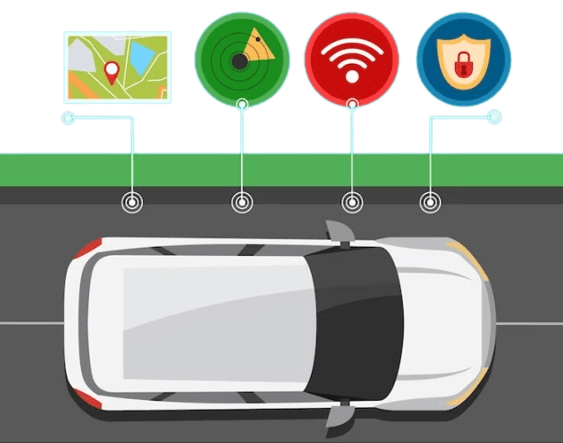
A safe and secured driving experience
Quick-to-deploy, codeless mobile application security enhances data connectivity and interoperability between the driver’s phone, the connected car and the manufacturer’s digital networks, securing the entire journey from A to Z.
Hardening both external and internal mobile applications reduces the attack surface, and runtime application self-protection (RASP) autonomously monitors, detects and manages unwanted activity, preventing tampering with devices connected to the vehicle’s onboard digital systems.
No compromise to the driver’s connected experience
Ensure driver safety and the privacy of your loyal customers by securing the connection between user devices, connected devices and the vehicle’s onboard digital systems.
Request a consultationBenefits for automakers, OEMs and fleet operators
Design a robust, flexible platform that supports current and future services with security built into the driver’s app.
A safe and secured driving experience
Codeless protection that enhances data connectivity and interoperability between the driver’s phone, the connected car and your digital networks.
No compromise to driver connectivity
Prevent tampering and hacking of apps and devices connected to the vehicle’s onboard pipelines, with hardening that reduces attack surfaces and RASP that manages unwanted activity autonomously.
Adopt new global and local requirements
Standards such as UNECE WP.29 are being imposed on automakers, OEMs and auto-related vendors. SecIron’s dynamic protection helps you conform to current and upcoming requirements.
Boost secured driver applications
Ensure driver safety and privacy by securing the connection between end devices, connected devices and vehicle onboard systems.
See the attack as it happens
Real-time detection of tampered apps, hooking tools and rooted devices, with the build, region and device behind each one.
Codeless, CI/CD-ready
Protection applied to the compiled build in your pipeline, so hardening ships at your release speed rather than on a separate project timeline.

Three solutions for the whole lifecycle
Assess before release
Automated vulnerability assessment against OWASP MASVS, with remediation guidance for every finding.
Explore IronSCAN →
Harden the binary
Multi-layer, codeless hardening: obfuscation, encryption, anti-tampering and RASP, applied to the compiled app.
Explore IronWALL →
Monitor in the field
Real-time detection and response across every session, with an audit-ready incident record.
Explore IronSKY →Automotive mobile app security, asked and answered
Why does the driver’s app need hardening if the vehicle is secure?
Because the app holds the keys. Pairing secrets, vehicle commands and account credentials sit in the app on a phone you do not manage. An attacker who decompiles or modifies it can speak to the vehicle and your back-end as if they were the driver.
How does it stop a tampered app controlling the car?
Anti-repackaging and integrity verification detect a modified or re-signed build at launch, and runtime protection detects rooted devices, hooking frameworks and emulators, so the response policy you set can block commands before they reach the vehicle.
Does it help with UNECE WP.29 and cybersecurity management requirements?
It delivers the application-layer controls and the evidence: hardened and monitored mobile apps with a timestamped incident log that supports your cybersecurity management system documentation.
Does it cover dealer and service apps as well as consumer apps?
Yes. Hardening applies to both external and internal mobile applications, so technician, dealer and fleet tools get the same protection as the customer app.
Does it require changes to our source code?
No. Protection is applied to the compiled APK, AAB or IPA as a step in your build pipeline, with no SDK to integrate and nothing for your developers or suppliers to rewrite.
Resources for automotive security teams
 BlogSecuring mobile apps with multi-layered security strategies for emerging threatsRead the article
 BlogWhy data encryption is essential to secure digital ecosystemsRead the article
 BlogMobile app security trends and strategic solutions in 2026Read the article
 WhitepaperRuntime Application Self Protection (RASP): the next step up to app securityRead the guide
 Internet of ThingsIndustryInternet of ThingsSee the industryUtilitiesIndustryUtilitiesSee the industry
Ready to secure your connected-car app?
From deployment to security and beyond, SecIron takes you from visibility to action. Bring us your driver app and we will show you what an attacker sees, then what they see once it is protected.
End-to-end mobile application security. Assess, harden and monitor Android and iOS apps with codeless integration.