13 Oct
iOS App Protection: A Practical Guide
iOS is harder to attack, which produces the most common planning mistake: treating harder as handled. What the platform gives you, what survives anyway, and the five iOS priorities.
12 Oct
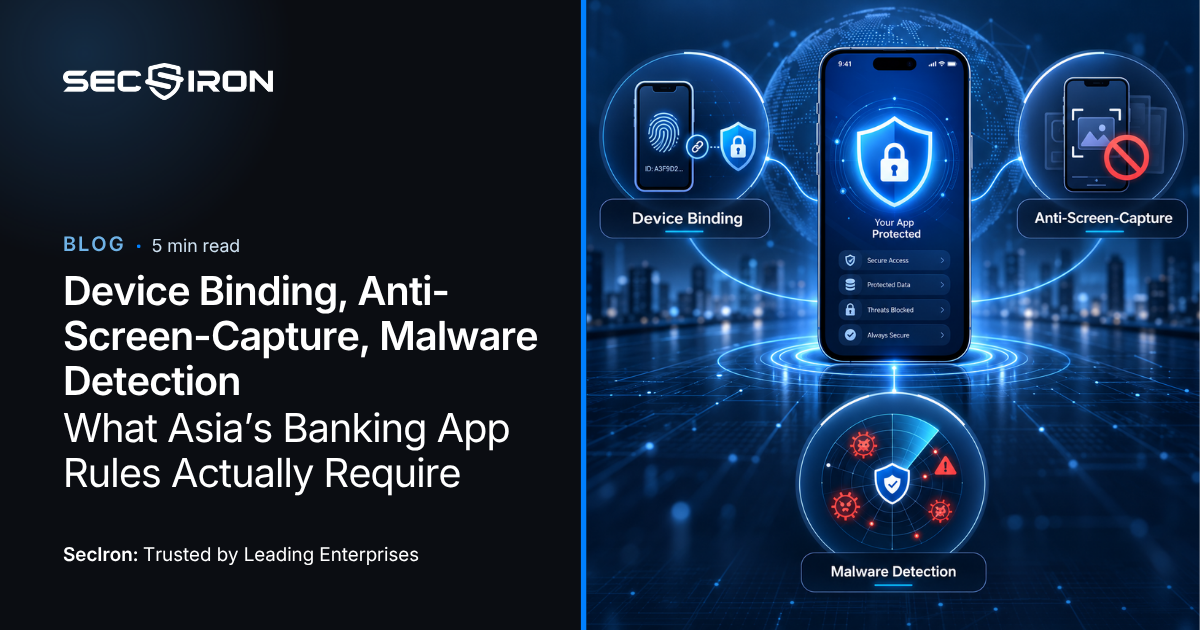
Device Binding, Anti-Screen-Capture, Malware Detec...
BNM RMiT, MAS TRM, HKMA and BSP converge on the same mobile app controls. What device binding, anti-screen-capture and malware detection actually require, and what examiners ask to see.
08 Oct
Root and Jailbreak Detection: How It Works and How...
Almost every banking app has root detection, and much of it can be bypassed from a public guide. How the four detection methods work, the three bypass approaches, and what actually holds.
06 Oct
Mirax in Malaysia: How This Android Remote Access ...
A Facebook ad for cheap goods, a phone call, a remote access trojan, and six figures gone. The Mirax attack chain stage by stage, and why controls positioned away from the device report nothing.
04 Oct
Android App Protection: A Practical Guide
Android carries more threat activity for structural reasons. What makes the platform different, the six Android-specific attacks, why ProGuard is only layer one, and a practical priority order.
01 Oct
What Is Anti-Tampering? How Apps Detect Modificati...
Anti-tampering is how an app knows it is no longer the app you shipped. The four detection mechanisms, why each fails alone, and what the app should do once it knows.
27 Sep
Runtime App Protection: What Your App Sees While I...
The specific signals a protected app produces while it runs, what confidence each carries, and how aggregating them turns session defence into threat intelligence about your own user base.
24 Sep
Zero-Day Attacks on Mobile Apps: What Real-Time Th...
Zero-day attacks on mobile apps use techniques no signature has catalogued yet. How behaviour-based detection closes the gap, and what real-time visibility looks like.
18 Nov
Mobile App Security Trends and Strategic Solutions...
AI-written phishing, deepfakes against identity checks, NFC relay fraud and a surge in banking trojans: the mobile app security trends shaping 2026, and the strategies that answer them.
Recent Posts

Mobile Application Hardening: Build vs Buy
October 18, 2026
Certificate Pinning: Why It Fails and What to Pair It With
October 15, 2026
Employee Highlight: Muhammad Iqbal
October 13, 2026