29 Oct
Guide: Protecting Mobile Apps Against Malware
A practical 16-page guide for security and engineering teams: what mobile malware actually does to your app, why server-side controls cannot see it, the six features to demand, and how to build a defence on devices you do not own.
29 Oct
Self-Assessment: 20 Questions to Assess Your Mobil...
A diagnostic, not a quiz. Twenty questions for security decision-makers across six sections, with a scoring sheet and the five gaps it usually exposes. Fifteen minutes will tell you where your mobile apps are exposed. Download the full assessment.
29 Oct
Use Cases: Three Real Attack Scenarios from SecIro...
Three real attack scenarios from SecIron deployments: HTTPS hijacking at a bank, silent reconnaissance ahead of an attack, and location fraud at a telco. What each one looked like on the device, and how it was caught. Download the full
29 Oct
NFC Relay and Ghost Tap: The New Payment Fraud Cha...
NFC relay borrows a real card in real time rather than stealing it for later. The five-step chain, why card fraud analytics cannot see it, and what detects it on the device.
28 Oct
Banking Case Study: How an International Bank Met ...
A Taiwan-based international bank had weeks to meet a central-bank mandate for mobile app protection. See how it hardened its app on-premise, codeless, with the first protected app live in two weeks. Download the full case study.
25 Oct
Mobile Reverse Engineering: How Attackers Read You...
Mobile reverse engineering is the first step in almost every serious attack on an app. Static versus dynamic analysis, what each platform gives up, what AI changed, and how to defend both halves.
22 Oct
Top Mobile App Security Threats For The Banking In...
Top Mobile App Security Threats For The Banking Industry Digitalization is in full swing in the fintech, eWallet providers, and banking industry, and it’s brought along numerous benefits to financial institutions. Lack of security is a significant problem for all
22 Oct
A 30-Day Mobile App Compliance Preparation Plan
A four-week plan to move from having mobile app controls to proving them. Inventory, harden, learn from your telemetry, then enforce, with the evidence pack an examiner asks for.
22 Oct
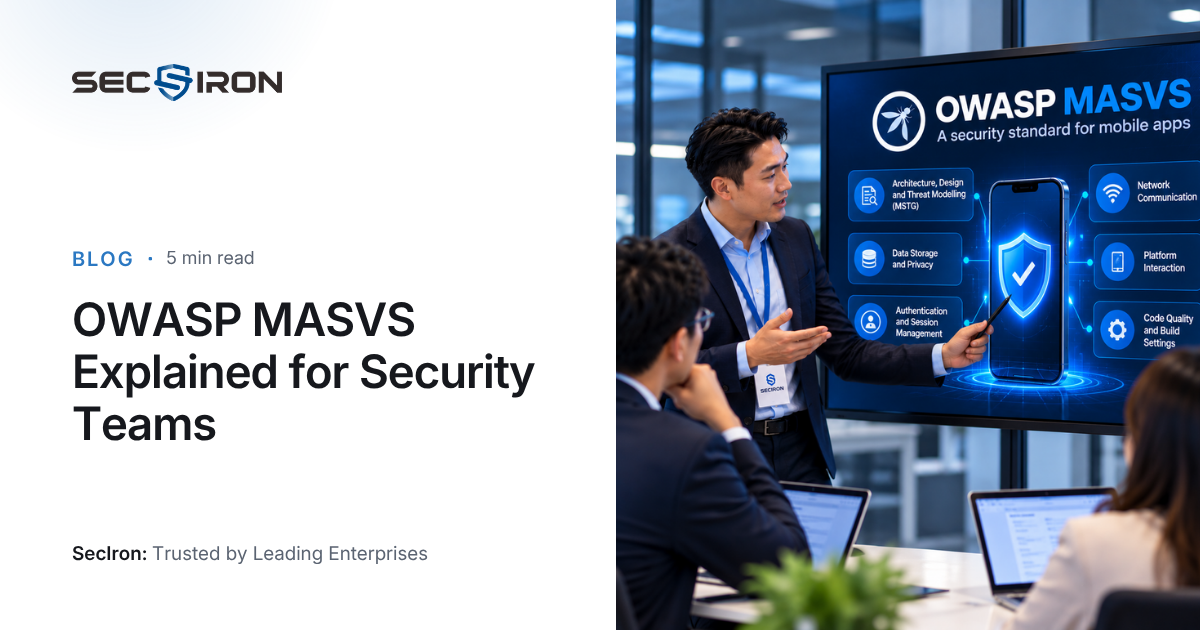
OWASP MASVS Explained for Security Teams
OWASP MASVS is cited more often than it is read. What the control groups cover, why the resilience group changes the conversation, and how to use it without creating a spreadsheet.
18 Oct
Mobile Application Hardening: Build vs Buy
Any competent team can build hardening. Few can maintain it through four OS releases while shipping a roadmap. The recurring costs, when building is right, and the hybrid most teams land on.
Recent Posts

Insurance App Hardening: Protecting Underwriting Logic and Claims
November 19, 2026
E-Commerce App Hardening: Protecting Promotions, Loyalty and Checkout
November 12, 2026
Employee Highlight: Haekal
November 10, 2026