15 Oct
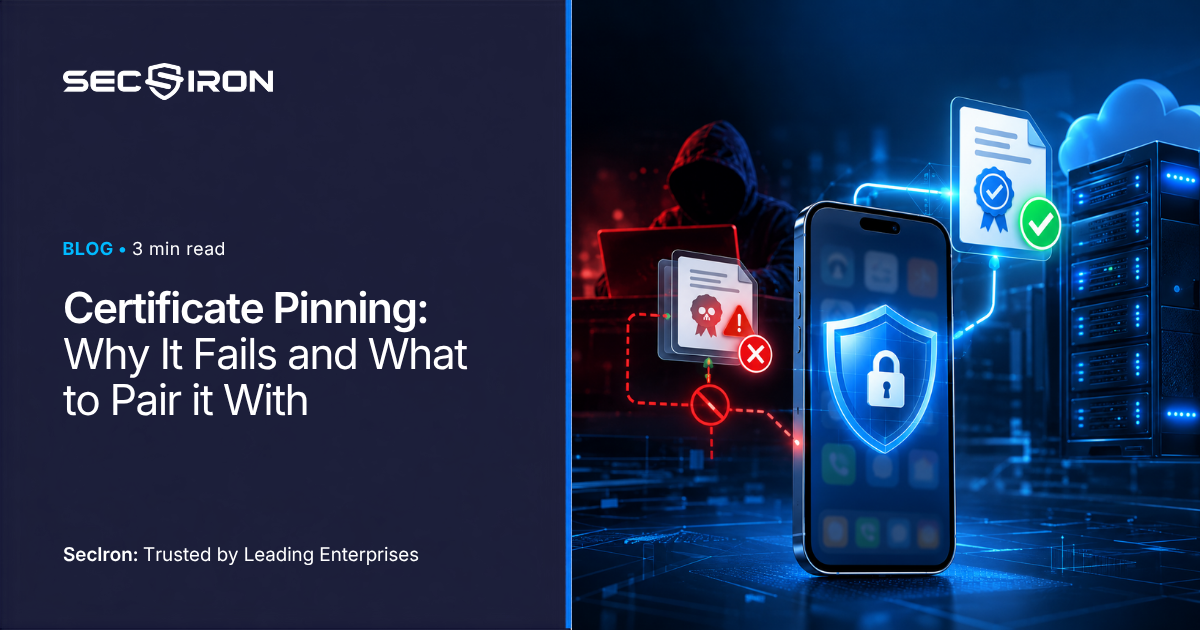
Certificate Pinning: Why It Fails and What to Pair...
Certificate pinning is bypassed routinely, and not because the cryptography is weak. Why the check is the target, the two operational failures, and the four controls to pair it with.
13 Oct
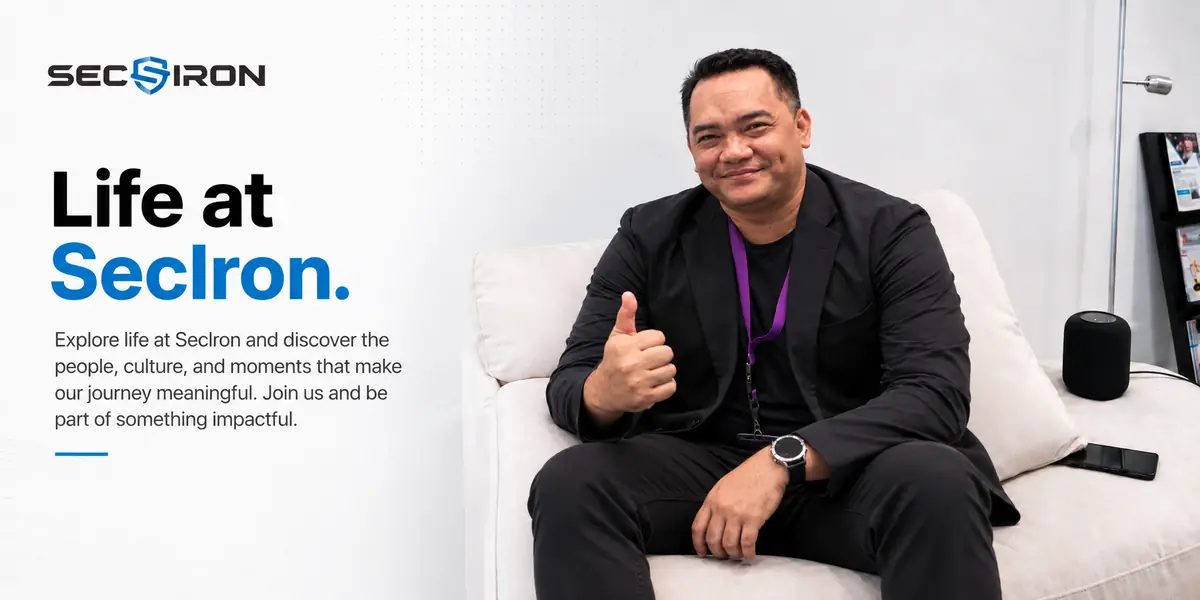
Employee Highlight: Muhammad Iqbal
Muhammad Iqbal, Country Manager, Indonesia, on how mobile application security has moved up the agenda there, what companies overlook when they protect their apps, and why trust in a relationship-driven market comes down to delivering what you promise.
11 Oct
iOS App Protection: A Practical Guide
iOS is harder to attack, which produces the most common planning mistake: treating harder as handled. What the platform gives you, what survives anyway, and the five iOS priorities.
08 Oct
Root and Jailbreak Detection: How It Works and How...
Almost every banking app has root detection, and much of it can be bypassed from a public guide. How the four detection methods work, the three bypass approaches, and what actually holds.
06 Oct
Mirax in Malaysia: How This Android Remote Access ...
A Facebook ad for cheap goods, a phone call, a remote access trojan, and six figures gone. The Mirax attack chain stage by stage, and why controls positioned away from the device report nothing.
04 Oct
Android App Protection: A Practical Guide
Android carries more threat activity for structural reasons. What makes the platform different, the six Android-specific attacks, why ProGuard is only layer one, and a practical priority order.
01 Oct
What Is Anti-Tampering? How Apps Detect Modificati...
Anti-tampering is how an app knows it is no longer the app you shipped. The four detection mechanisms, why each fails alone, and what the app should do once it knows.
26 Oct
Mobile Application Security: A Complete Guide for ...
Mobile application security explained: the threats facing Android and iOS apps, the OWASP Mobile Top 10, five layers of protection and how to choose a vendor.
Recent Posts

Insurance App Hardening: Protecting Underwriting Logic and Claims
November 19, 2026
E-Commerce App Hardening: Protecting Promotions, Loyalty and Checkout
November 12, 2026
Employee Highlight: Haekal
November 10, 2026